Three fines that do not create a pricing schedule
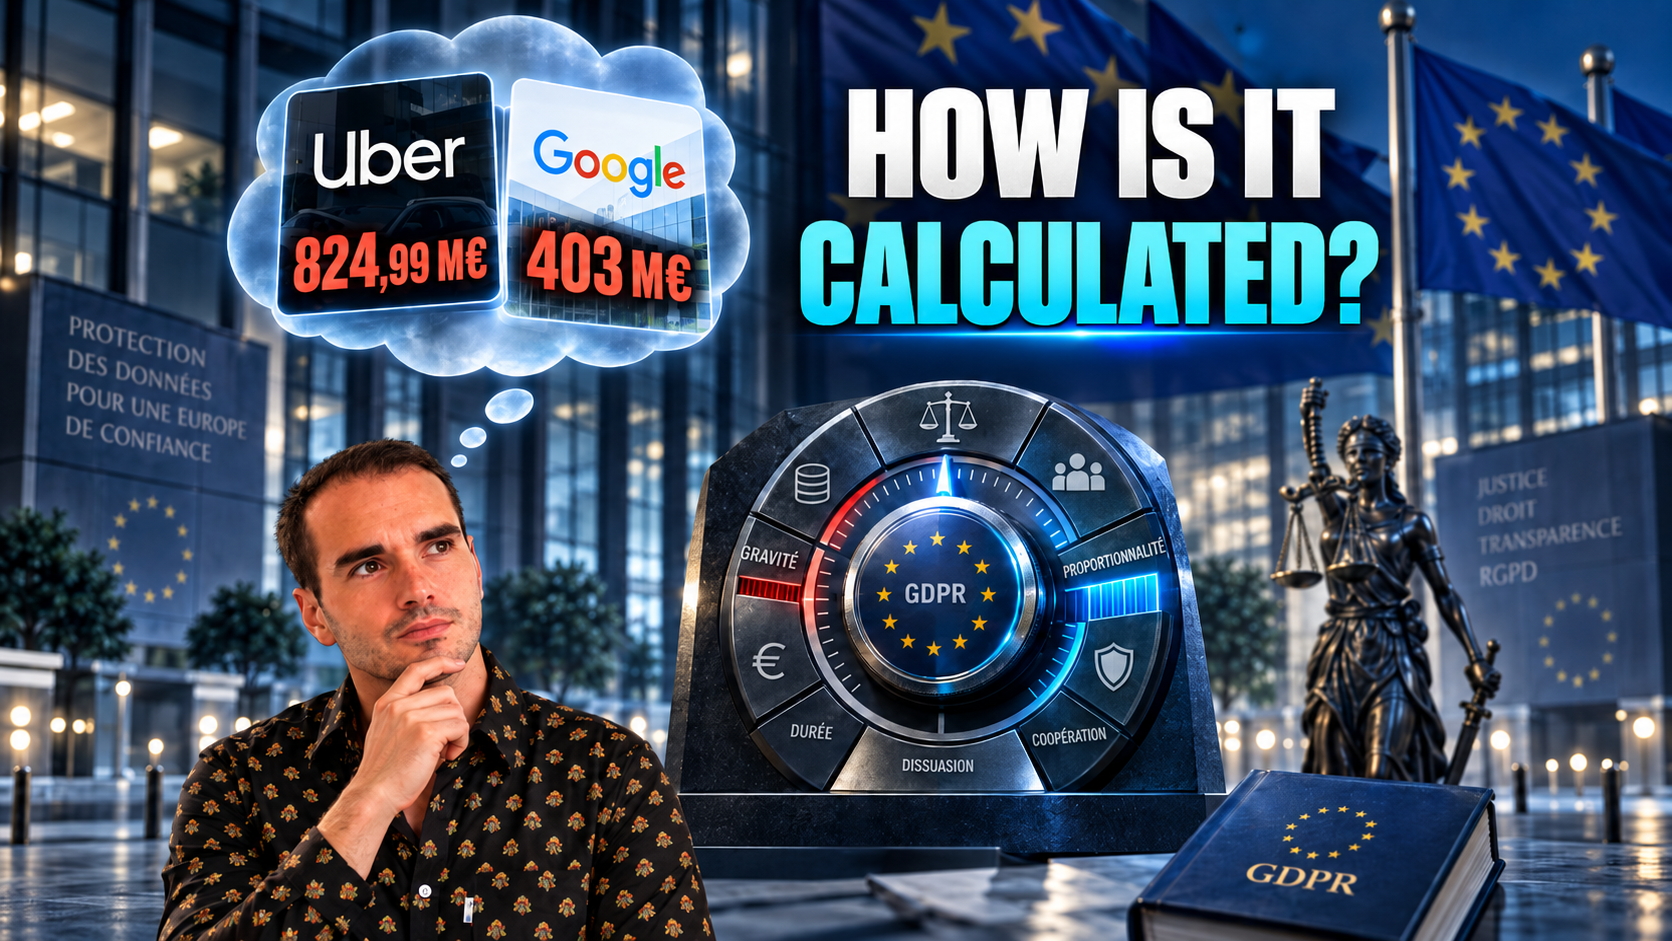
An €824.99 million penalty against Uber, €403 million against Google, and €5 million against IQVIA Operations France naturally prompt a boardroom question: “What would our exposure be?”
| Organization | Fine announced in 2026 | Main issue and dated official source |
|---|---|---|
| Uber B.V. and Uber Technologies Inc. | €824.99 million | Automated driver decisions, sanctioned by the Dutch authority. CNIL, Uber Enforcement Announcement, August 24, 2026 (French) |
| Google Ireland Limited | €403 million | Location-data processing. DPC, Google Enforcement Announcement, September 21, 2026 |
| IQVIA Operations France | €5 million | Health-data warehouses, transparency and required safeguards. CNIL, Decision SAN-2026-008, May 26, 2026 (French) |
These are enforcement announcements, not comparable prices for a GDPR violation or predictions of the outcome of any judicial challenge.
For a U.S. business, the first question remains whether the relevant processing falls within GDPR, Article 3. Covered activities include processing in the context of an EU establishment and certain processing connected to offering goods or services to people in the EU or monitoring their behavior there. U.S. incorporation is not, by itself, an exemption.
What changed at the September 17 EDPB meeting?
The European Data Protection Board coordinates consistent GDPR application by national supervisory authorities. Its EDPB, Draft Guidelines 04/2026, September 17, 2026 address the decision to impose an administrative fine in relation to other corrective powers.
They interpret existing law rather than amend the GDPR. The EDPB, Public Consultation Closing November 13, 2026 confirms that this document is still a draft as of the review date above.
The CNIL, September 17, 2026 EDPB Plenary Summary (French) describes five checks and 14 practical examples. The first three checks concern legal preconditions; the final two address whether a fine is appropriate.
- Is the infringement legally finable? The authority identifies the relevant GDPR or national-law provision.
- Which entity can be fined? Responsibility depends on who was bound by the breached obligation, including controllers and processors.
- Was the conduct intentional or negligent? A culpable infringement is required; negligence can be sufficient.
- Is the infringement minor? The authority considers seriousness, duration, affected people, data categories, prior infringements and mitigation.
- Would a fine be appropriate? It must be effective, proportionate and dissuasive in the individual circumstances.
Intentional or negligent conduct is not a new requirement created by the draft. The Court of Justice confirmed that condition in CJEU, December 5, 2023, Deutsche Wohnen, C-807/21. A company does not have to intend to harm individuals to be exposed to a fine.
When might a reprimand be enough?
The draft generally points toward a reprimand rather than a fine for a minor infringement. For a non-minor infringement, it establishes a strong presumption in favor of a fine. Neither outcome is automatic.
This helps legal teams organize a substantive response. The relevant arguments concern the actual conduct, the severity of the infringement and the suitability of the proposed measure, not simply a general assertion of good intentions. Prompt remediation is relevant, but does not retroactively make the original processing lawful.
How is the amount calculated?
The EDPB, Guidelines 04/2022 on the Calculation of Administrative Fines, Version 2.1, finalized on May 24, 2023, remain the separate framework for calculating the amount.
The approach identifies the processing operations and any multiple infringements, establishes a starting point reflecting seriousness and turnover, evaluates aggravating and mitigating circumstances, checks the statutory ceilings, and tests the final amount for proportionality, effectiveness and deterrence.
Under GDPR, Article 83, the principal ceilings are €10 million or 2% of total worldwide annual turnover for the preceding financial year, and €20 million or 4%, depending on the provisions breached. For an undertaking, the higher figure within the applicable tier is the ceiling, not an automatic penalty.
U.S. groups should not assume that exposure is measured only against European revenue. The concept of an undertaking can make group-wide worldwide turnover relevant, as explained in the Deutsche Wohnen judgment cited above.
A reasoned estimate is possible; a reliable one-click prediction is not. Binding supervisory decisions remain subject to judicial challenge under GDPR, Article 78.
Remediation can change the remedy without erasing the violation
The IQVIA decision illustrates the distinction. The CNIL accepted that certain security shortcomings had been corrected and did not impose a further compliance order for those issues. It nevertheless imposed a fine and required other deficiencies to be remedied, backed by periodic penalty payments.
For general counsel, the practical implication is to build an evidence file rather than rely on a statement that the problem has been fixed. A useful file can include the incident chronology, the allocation of responsibilities, earlier warnings, steps taken to limit harm and tests showing that the changes work.
This is a preparation framework, not a guaranteed discount mechanism. Its value is that the company can explain both what happened and which further measures are genuinely necessary.
The bigger business risk may be the order accompanying the fine
GDPR, Article 58 allows authorities to order compliance, restrict or prohibit processing, and suspend transfers to a third country. Those measures can accompany a fine.
The Google announcement provides a concrete example: the Irish DPC imposed €403 million in fines and required Google to bring its processing into compliance within six months.
For a U.S. company dependent on European customer data, a processing restriction or transfer suspension can require a service redesign. A risk assessment should therefore model the remediation and continuity consequences, not just the maximum financial penalty.
Why the DSA does not replace GDPR compliance
At the same plenary meeting, the EDPB adopted the EDPB, Guidelines 3/2025 on the DSA and the GDPR, Final Version of September 17, 2026. Unlike the fine-imposition draft, this document is final.
The guidelines address consistent application where obligations under the Digital Services Act involve personal-data processing by intermediary service providers. Compliance with a DSA obligation is not a general exemption from the GDPR.
As a practical illustration, collecting information to verify a marketplace seller does not automatically authorize its later use for advertising. The purpose, legal basis, necessary information and retention period must still be assessed. The DSA and GDPR remain distinct compliance regimes, not interchangeable rules.
What U.S. legal teams should take away
The useful distinction is between whether an authority may fine, whether it should fine, and how much it should impose.
The 2026 draft makes the second question more structured. It does not turn enforcement into a predictable price for doing business. For legal teams, the actionable work is to document the facts, substantiate mitigation and plan for restrictions on processing. A fine can be budgeted; an unprepared interruption to a critical data flow can be much harder to absorb.
Did the EDPB introduce a new GDPR fine formula in 2026?
No. Draft Guidelines 04/2026 concern whether to impose a fine in relation to other corrective measures. Guidelines 04/2022, finalized in 2023, concern the amount.
Is the September 2026 draft already final?
Not as of October 4, 2026. Consultation closes on November 13, 2026. The separate DSA/GDPR guidelines adopted at the same meeting are final.
Does fixing the problem prevent a fine?
Not automatically. Remediation can affect the regulator’s assessment and the corrective measures still needed, but does not erase an earlier infringement.
Is a GDPR fine automatically 4% of revenue?
No. The applicable ceiling depends on the breached provisions. The amount is individually assessed, and non-financial corrective measures may also apply.