
Executive Summary
Conducting due diligence in China is no longer only about collecting enough information to assess a supplier, business partner, acquisition target, or customer.
The investigation itself may create legal risk.
European companies are expected to verify beneficial ownership, sanctions exposure, corruption risks, supply-chain conditions, export-control restrictions, and links with public authorities or state-owned enterprises.
At the same time, Chinese law increasingly regulates how information may be collected, transferred outside China, or used to implement foreign sanctions and regulatory measures.
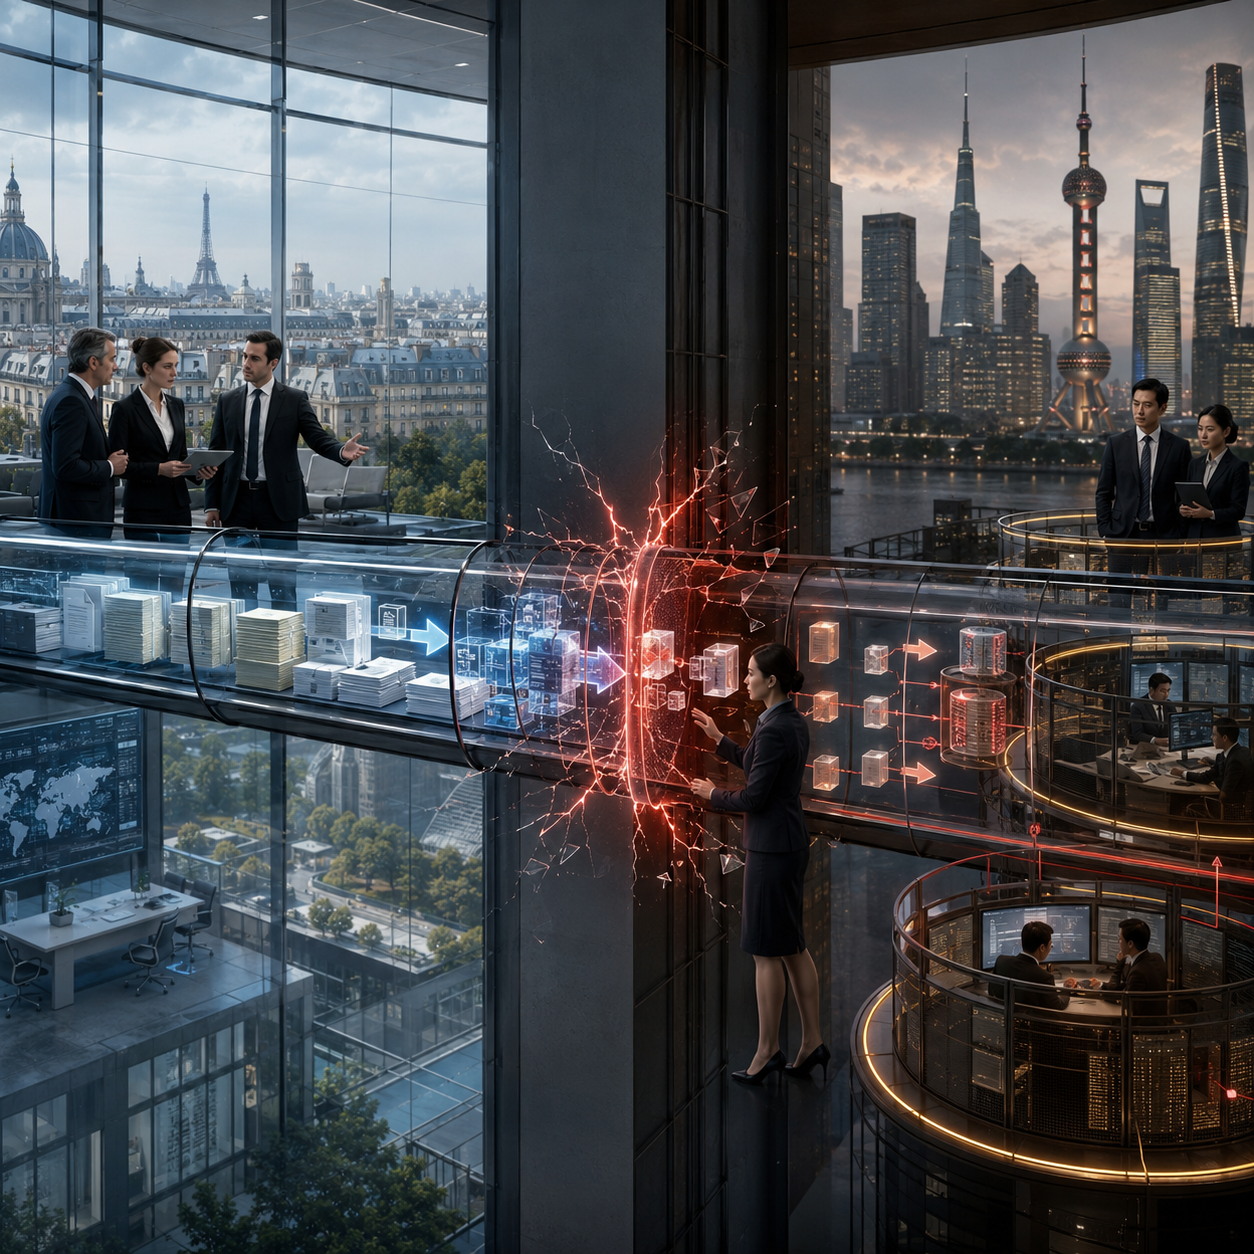
This creates a practical conflict of laws.
A request that appears routine to a European headquarters may place a Chinese subsidiary, employee, or business partner in a difficult position.
The solution is not to abandon due diligence. It is to redesign it.
Companies operating in China should move away from standardized global questionnaires and adopt a risk-based process that distinguishes the purpose of the investigation, the nature of the information requested, the location of the data, the identity of the recipient, and the legal consequences of using the information.
A defensible due diligence process is no longer the one that collects the most information.
It is the one that obtains the necessary information through methods that are proportionate, locally lawful, documented, and capable of protecting both the group and its local teams.
Key Takeaways
European and Chinese legal requirements may pull companies in opposite directions.
European sanctions, anti-corruption, export-control, and supply-chain due diligence rules require companies to investigate third parties and business relationships.
Chinese rules on personal information, data security, state secrets, counter-espionage, and foreign sanctions may restrict how certain information is collected, transferred, or used.
The Chinese legal framework does not prohibit all internal investigations or cross-border data transfers. Each step must be assessed separately.
A company should distinguish between collecting information in China, transferring it within the group, and providing it to a foreign regulator or court.
Oral communication does not automatically avoid data-transfer restrictions.
Contracts should include consultation, suspension, hardship, change-in-law, and escalation mechanisms rather than imposing unlimited compliance with every foreign sanctions regime.
When information cannot lawfully be obtained, the company should document the obstacle, assess the residual risk, and determine whether alternative verification measures are available.
Quick Answer: Can European Companies Conduct Due Diligence in China?
Yes, European companies can conduct due diligence in China.
However, they should not assume that a questionnaire, investigation method, or reporting process designed in Europe can be used unchanged in China.
The legality of the process depends on several factors:
- why the information is being requested;
- whether it includes personal or sensitive data;
- where the information is stored;
- who will receive it;
- whether it may be provided to a foreign authority;
- whether it relates to state security, strategic sectors, public bodies, or sanctioned entities;
- and whether the resulting decision would implement a foreign restrictive measure prohibited under Chinese law.
The safest approach is to structure the review locally, minimize the information collected, validate sensitive requests with Chinese counsel, and document any limitation that prevents the group from obtaining a complete answer.
Why Due Diligence in China Creates a Conflict of Laws
European companies face increasing expectations to understand their counterparties and supply chains.
Depending on the transaction, they may need to identify:
- beneficial owners;
- directors and key decision-makers;
- links with sanctioned persons;
- ownership or control by public authorities;
- intermediaries and end users;
- the origin and destination of products;
- working conditions;
- corruption exposure;
- export-control risks;
- and possible human-rights or environmental impacts.
These investigations may be required or encouraged by sanctions programs, export-control rules, the French Sapin II law, the French Duty of Vigilance Law, European corporate sustainability due diligence rules, internal compliance policies, or contractual obligations.
Chinese law creates a different set of priorities.
It protects personal information, regulates important data, restricts certain disclosures to foreign authorities, reinforces state-security controls, and limits the implementation of some foreign sanctions against Chinese persons and companies.
The resulting tension is structural.
European law may require the company to know more.
Chinese law may require the company to collect less, transfer differently, or avoid using the information for a prohibited purpose.
The Main Chinese Legal Frameworks
Personal Information Protection Law
China’s Personal Information Protection Law, commonly known as the PIPL, regulates the processing of personal information and imposes requirements on transfers outside China.
A due diligence investigation may involve personal information when it identifies directors, employees, beneficial owners, intermediaries, representatives, or other individuals connected with a business partner.
Before transferring such data, companies may need to consider:
- the legal basis for the processing;
- whether the information is necessary;
- the information provided to the individuals;
- separate consent where applicable;
- contractual or certification mechanisms;
- security assessments;
- and the safeguards applied by the overseas recipient.
The applicable mechanism depends on the nature and volume of the data, the identity of the processor, and the regulatory framework in force.
Data Security Law
The Data Security Law applies more broadly to data-processing activities and creates particular sensitivity around important data, national security, and disclosures to foreign authorities.
Article 36 is especially relevant when a foreign court, regulator, prosecutor, or administrative authority requests data stored in China.
An organization or individual in China should not provide such data directly to a foreign judicial or law-enforcement authority without approval from the competent Chinese authorities.
This rule should not be confused with a general prohibition on all intra-group transfers.
A transfer to a European headquarters and a disclosure to a foreign regulator are legally distinct operations and should be analyzed separately.
State Secrets and Counter-Espionage Rules
Due diligence becomes more sensitive when it concerns:
- strategic sectors;
- advanced technologies;
- public authorities;
- state-owned enterprises;
- critical infrastructure;
- industrial policies;
- supply-chain security;
- or information that may be connected to national security.
China’s state-secrets and counter-espionage frameworks may affect the collection or transmission of documents and economic information in these areas.
This does not mean that every corporate investigation creates an espionage risk.
It means that the scope, sources, personnel involved, and reporting channels require greater caution.
Anti-Foreign Sanctions Law
China’s Anti-Foreign Sanctions Law creates another layer of conflict.
Article 12 restricts organizations and individuals from implementing or assisting in the implementation of discriminatory restrictive measures imposed by foreign states against Chinese persons or organizations.
A decision published by the Chinese Supreme People’s Court in 2026 showed that this framework can have concrete contractual consequences.
In that case, a carrier refused to perform obligations toward a Hong Kong company because of a foreign sanctions list. The Shanghai Maritime Court treated Article 12 as a mandatory rule and awarded compensation to the counterparty.
The lesson is significant.
Complying with a foreign sanctions measure may not automatically excuse non-performance under Chinese law.
Why Local Employees May Be Reluctant to Respond
European headquarters may interpret incomplete answers as a warning sign.
Sometimes they are.
In China, however, reluctance may also reflect legal uncertainty.
A local employee may hesitate to confirm:
- whether a partner is linked to a state-owned enterprise;
- whether a person appears on a foreign sanctions list;
- whether sensitive technology has been transferred;
- whether a supplier operates in a politically sensitive region;
- or whether information may later be shared with a foreign regulator.
The employee may fear that the response could facilitate a foreign restrictive measure, disclose protected data, or create personal exposure.
This possibility should not eliminate scrutiny.
It should change the method of scrutiny.
The company should distinguish between deliberate concealment, an inability to verify, and a legitimate local-law restriction.
Why Standard Global Questionnaires Are Dangerous
Global questionnaires offer consistency, but they often ignore territorial legal differences.
A form designed at European headquarters may request:
- excessive personal information;
- data unrelated to the specific risk;
- documents that cannot lawfully leave China;
- written confirmation of foreign sanctions compliance;
- or broad representations concerning government connections.
The problem is not only the wording of the questionnaire.
It is the entire information flow.
Who receives the answers?
Where are they stored?
Will they be incorporated into a global compliance database?
Could they be disclosed to a European or US authority?
Will they be used to terminate a Chinese contract?
Each stage may raise a different legal issue.
A Better Due Diligence Method for China
Define the exact purpose
The investigation should begin with a clearly defined objective.
A sanctions review, anti-corruption assessment, acquisition audit, export-control check, and human-rights review do not require identical information.
Broad requests such as “provide all information relevant to compliance” should be avoided.
Limit collection to what is necessary
The company should identify which data points are essential and which are merely convenient.
Collecting less information can reduce data-protection and national-security risk without weakening the quality of the assessment.
Separate local review from cross-border reporting
Sensitive documents may be reviewed locally, with only a filtered legal conclusion or risk summary transferred to headquarters.
This model can reduce unnecessary data transfers while allowing the group to make an informed decision.
Validate sensitive requests locally
Requests involving public authorities, state-owned companies, strategic technologies, sanctions, or sensitive data should be reviewed by local counsel before they are sent.
Map the complete data flow
The group should document:
- where the information originates;
- who collects it;
- where it is stored;
- who may access it;
- whether it leaves China;
- and whether it could later be disclosed to an authority.
Create an escalation mechanism
Local employees should have a clear process for raising concerns without appearing to obstruct the investigation.
The escalation path may involve local legal counsel, regional compliance, headquarters, and senior management.
Document unavailable information
A missing answer should not disappear from the file.
The company should record:
- what was requested;
- why it was necessary;
- why it could not be obtained;
- which alternative sources were reviewed;
- and what residual risk remains.
This documentation may be critical if the decision is later challenged.
Oral Communication Does Not Eliminate the Risk
Some organizations try to avoid written transfers by discussing sensitive information by telephone or videoconference.
This is not a complete solution.
Information communicated orally can still cross a border.
The absence of an email attachment does not necessarily remove the application of data-transfer or secrecy rules.
Oral reporting also creates an evidentiary problem.
Companies should use controlled internal notes that distinguish:
- facts confirmed by reliable sources;
- statements made by the local team;
- legal interpretations;
- and information that remains uncertain.
The goal is to create sufficient traceability without reproducing unnecessary sensitive data.
Contracts Must Reflect the Conflict of Laws
Contracts should not assume that every foreign sanctions regime can always be applied without limitation.
A broad clause requiring a Chinese counterparty to comply with all current and future foreign sanctions may create legal and enforcement difficulties.
More tailored mechanisms may include:
- consultation obligations;
- notification of conflicting legal requirements;
- temporary suspension rights;
- change-in-law clauses;
- hardship clauses;
- alternative performance;
- regulatory-approval conditions;
- and escalation procedures.
The contract should define what happens when performance is required under one legal system but restricted under another.
A well-drafted clause does not eliminate the conflict.
It gives the parties a process for managing it.
Implications for Mergers and Acquisitions
M&A due diligence in China may require access to employee data, customer information, commercial records, technical documents, public-sector contracts, and supply-chain information.
Before opening a virtual data room to an overseas buyer, the parties should assess:
- whether the documents contain personal information;
- whether sensitive or important data is involved;
- whether local review and redaction are required;
- whether regulatory approval may be necessary;
- and whether the prospective buyer’s advisers should receive full documents or summarized conclusions.
The pressure to complete a transaction quickly should not override the need to structure the data-transfer process lawfully.
What European Legal Departments Should Do
Legal and compliance teams should treat China-related due diligence as a separate workstream rather than a translation of the global process.
A practical framework should include:
- A China-specific due diligence protocol.
- A data and document classification matrix.
- Local-law review for sensitive requests.
- A cross-border data-transfer assessment.
- Clear rules for foreign-authority requests.
- Contract clauses addressing conflicting sanctions regimes.
- Escalation procedures for local employees.
- Evidence of unavailable or restricted information.
- Alternative verification sources.
- Periodic review as Chinese and European rules evolve.
Final Analysis
Due diligence in China remains possible.
The old method of maximizing information collection and centralizing every answer at headquarters is becoming increasingly difficult to defend.
The legal challenge is no longer only to determine whether a partner presents sanctions, corruption, export-control, or supply-chain risks.
Companies must also assess whether the investigation itself creates risks for the organization, its subsidiary, its employees, or its counterparties.
This changes the meaning of effective due diligence.
A strong process is not the one that produces the largest file.
It is the one that can demonstrate that each request was necessary, proportionate, locally lawful, properly validated, and documented.
In a conflict of legal systems, the absence of information cannot always be eliminated.
It must be governed.
Is due diligence prohibited in China?
No. Chinese law does not generally prohibit internal investigations or due diligence. However, the collection, transfer, and use of certain information may be restricted and should be assessed separately.
Can a Chinese subsidiary send personal data to its European headquarters?
Potentially, yes, but the transfer must comply with the PIPL and applicable cross-border data-transfer requirements.
What does Article 36 of China’s Data Security Law prohibit?
Article 36 restricts organizations and individuals in China from directly providing data stored in China to foreign judicial or law-enforcement authorities without approval from the competent Chinese authorities.
Can companies avoid cross-border transfer rules by communicating orally?
Not necessarily. Information may still be transferred across borders even when it is communicated by telephone or videoconference.
Can a company refuse to perform a Chinese contract because of foreign sanctions?
The answer depends on the circumstances. China’s Anti-Foreign Sanctions Law may restrict the implementation of certain foreign restrictive measures and may affect whether foreign sanctions justify contractual non-performance.
What should a company do when information cannot lawfully be obtained?
It should document the request, the legal obstacle, the alternative checks performed, and the residual risk. It should then decide whether the transaction can proceed with additional safeguards.